Assess
Gap Assessment
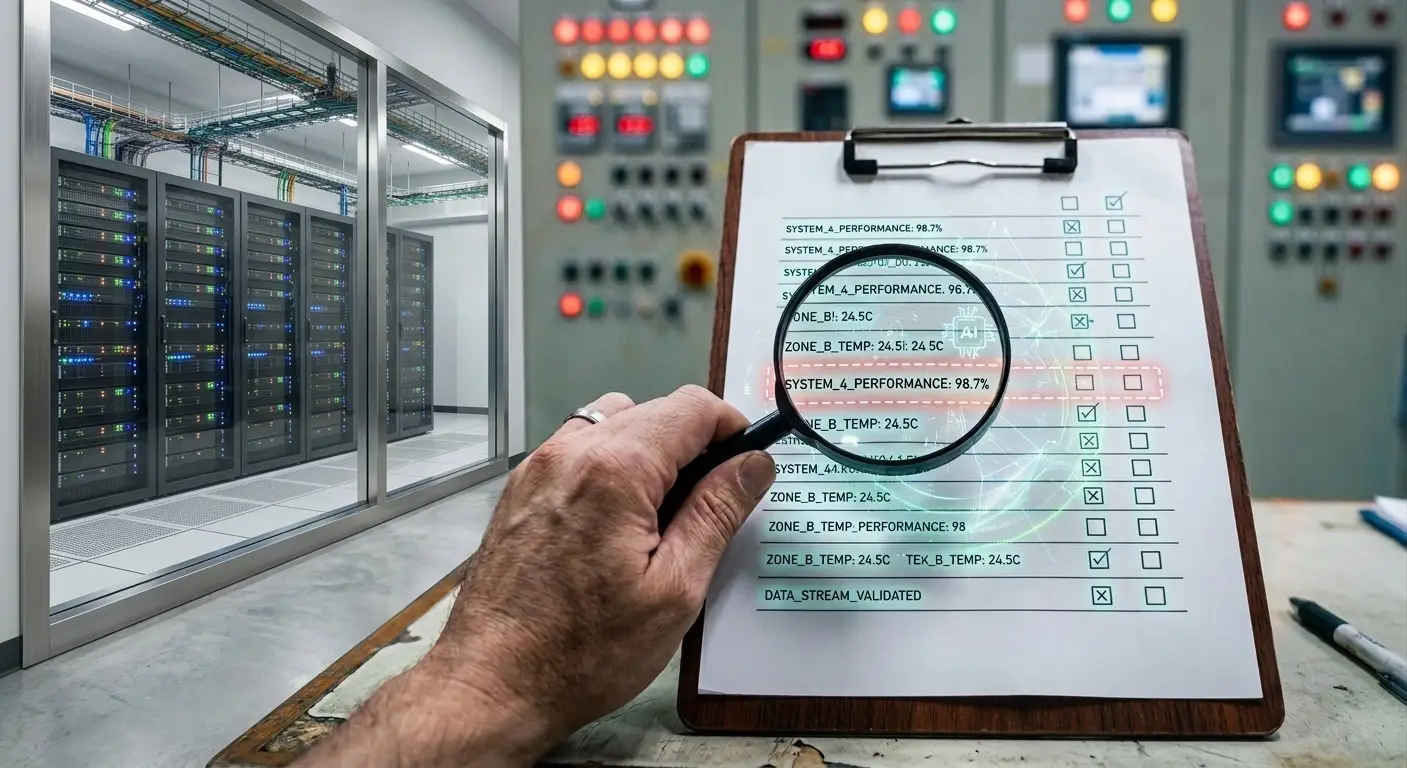
We measure your OT security programme against each element of IEC 62443-2-1 and tell you which gaps to close first and which can wait.
Our approach
- Stage 01AssessMeasure your exposure
- Stage 02DesignPlan the architecture
- Stage 03DeployInstall the technology
- Stage 04SustainMaintain security
Overview
What the service covers and why it matters
We assess your OT security programme against every element of the standard and record the evidence behind each score.
The result is a gap register that a contractor can work from and a roadmap you can present at a budget meeting, both ranked by risk.
- Standard
- IEC 62443-2-1
- Stage
- Assess, stage 1 of 4
- Usually follows
- Health check
- Sectors
- All
At a glance
What we look at
- Who is responsible for OT security, and what they are authorized to decide
- How changes to controllers are approved, and by whom
- How remote access by vendors is controlled
- How assets are recorded, and whether the records are current
- What the incident response plan covers in the first hour
- How the programme is measured, and who reviews the results
Why it matters
Spending decisions need evidence. A score against a published standard gives you a prioritized list of actions, each with an owner.
In most plants, security controls were added one project at a time by different contractors, and no one has a complete picture. This assessment brings it together in one place.
Auditors, insurers and major customers increasingly ask which standard you follow. For industrial operators, IEC 62443-2-1 is the recognized answer.
Scope
What this service does not include
- Not a technical scan.This assessment looks at the programme: who is responsible for what, how decisions are made and what is documented. The network itself is assessed separately.
- Not a certification.No certificate is issued. You receive a clear statement of your current position and a plan to improve it.
- Not a template exercise.The evidence is collected at your site, and the roadmap is built around your plant.
- No shutdown.We do not change or interrupt any running system during this work.
How it works
The steps and what you receive
- Scope agreed with the plant owners
- Drawings, policies and asset records reviewed
- Interviews on site with operations and engineering staff
- Controls checked against each element of the standard
- Scores assigned, with the supporting evidence recorded
- Roadmap ranked by risk and presented to the budget holders
What you receive
- Maturity scoresA rating for each element of the standard, with the evidence behind it.
- Gap and risk registerEvery finding, ranked, in a format you can hand to a contractor.
- RoadmapThe actions to take, in order of priority, with an owner for each one.
Who it is for
When this service is the right choice
- You have security controls in place but no measure of how effective they are
- You have been asked which standard you follow and need a clear answer
- You are planning a multi-year programme and need a baseline
- An insurer, auditor or customer has asked for evidence of your security position